If you want to see what burnout looks like in real time, sit next to an internal IT technician for thirty minutes on a Monday morning.
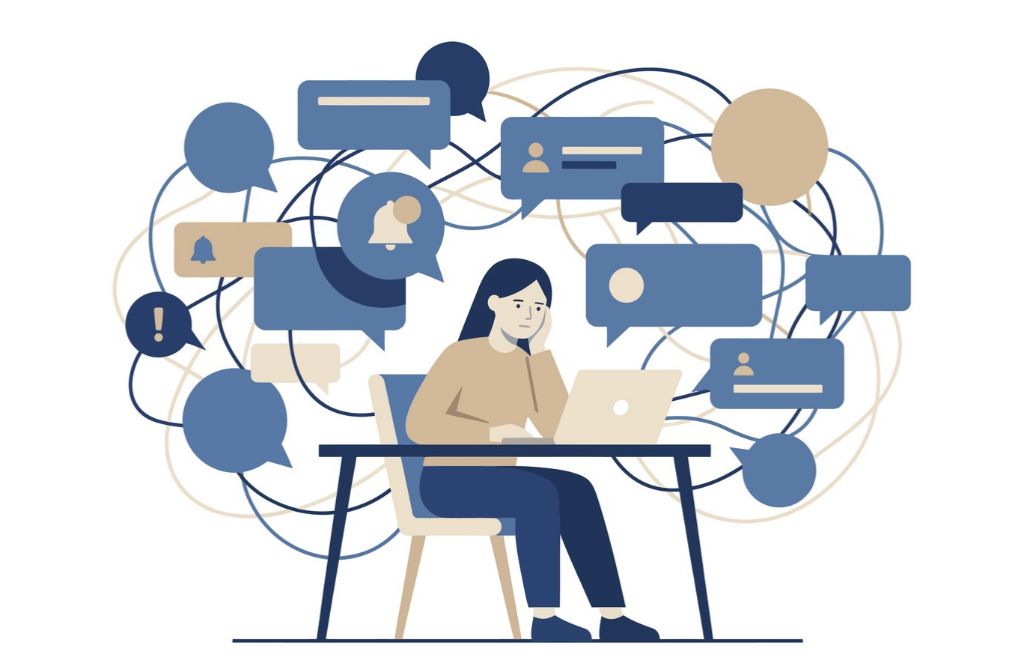
By 9:30 a.m., their monitor is usually flooded with dozens—sometimes hundreds—of automated security notifications. A printer lost connection on the second floor. A routine accounting software update triggered an unverified script flag. An employee typed their password wrong twice before their coffee kicked in.
When every single event generates a high-priority banner, basic human psychology takes over. It is the exact reason nobody looks out the window when a car alarm goes off in a parking lot. You do not assume a vehicle is being stolen; you just close your window and wish the noise would stop.
That desensitization is what we call alert fatigue, and in the world of business technology, it is one of the most dangerous vulnerabilities a company can develop.
The Boy Who Cried Malware
Security software hates taking chances. To protect itself from liability, modern endpoint detection tools are programmed to yell first and ask questions later.
If an internal IT department oversees 150 workstations and a handful of servers, that team can easily face 800 to 1,200 individual security events in a single workweek. Roughly 98% of those alerts are harmless false positives or routine background noise.
The problem is not the false alarms themselves. The problem is what sorting through that noise does to human focus.
When an IT generalist spends three hours a day clearing meaningless notifications, their brain enters triage autopilot. They click “dismiss,” “acknowledge,” and “ignore” just to keep the dashboard manageable. That cognitive depletion creates the exact gap attackers look for.
Modern cyberattacks rarely kick down the front door with flashing lights. Instead, bad actors favor “living-off-the-land” tactics. They use legitimate administrative utilities already built into Windows to quietly poke around files and map network shares.
To an overtired technician drowning in 200 other pop-ups, that quiet, stealthy lateral movement looks identical to a routine system script. By the time someone realizes it was not routine, the damage is already done.
Three Ways to Silence the Noise Without Sacrificing Safety
Fixing alert fatigue does not mean disabling notifications and crossing your fingers. It means refining your system so that only actionable, genuine threats demand your team’s attention.
Here is how businesses can get their sanity—and their security—back under control:
Establish a baseline of normal network activity. If your finance team runs a specific automated reporting script every Thursday at 4:00 PM, your monitoring software should expect it. Whitelisting known, legitimate processes eliminates recurring false positives immediately.
Tune alert thresholds aggressively. Not every event requires human eyes. A single failed login attempt does not warrant an emergency email. Ten failed attempts in thirty seconds from an IP address three states away? That requires immediate escalation. Configure your alerts so that severity matches reality.
Separate frontline support from security triage. Asking the same person who fixes jammed printers and configures new user accounts to also monitor active security telemetry is a recipe for missed signals. Security monitoring requires sustained, dedicated focus, not divided attention between helpdesk tickets.
Your internal staff has a finite amount of cognitive energy every day. If they spend that energy wading through digital false alarms, they will not have it when a sophisticated intruder slips through the cracks.
We believe technology should make your business more efficient, not bury your staff under an avalanche of useless notifications. If you want to ensure genuine threats are being caught before they cause downtime, give us a call at 978-798-6805.